Bypassing Using LOLBins
Living off the Land Binaries (LolBins) are legitimate system tools that are preinstalled on the operating system or downloaded from trusted sources such as Microsoft.
- Attackers can exploit these LoLBins for malicious purposes such as installing malware or maintaining persistence on target networks.
- By leveraging LoLBins, attackers can evade defensive solutions because their activities appear to be normal and authorized.
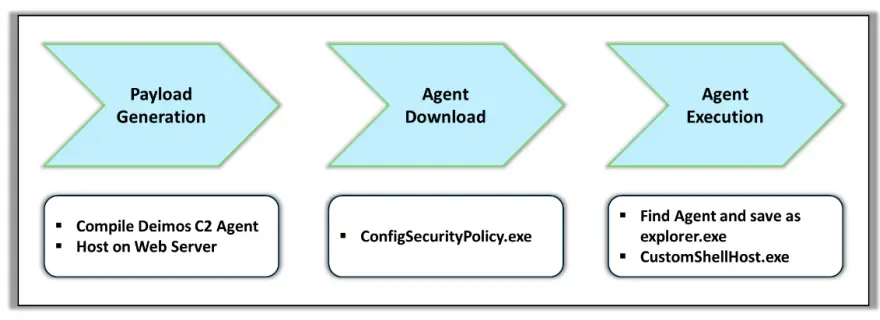
- These tools also help attackers execute various malicious activities, such as installing command and control (C2) agents for advanced post-exploitation control, without triggering alerts or being detected by endpoint detection and response (EDR) systems.