Lamport Clock
- A process is modeled as a sequence of totally ordered events.
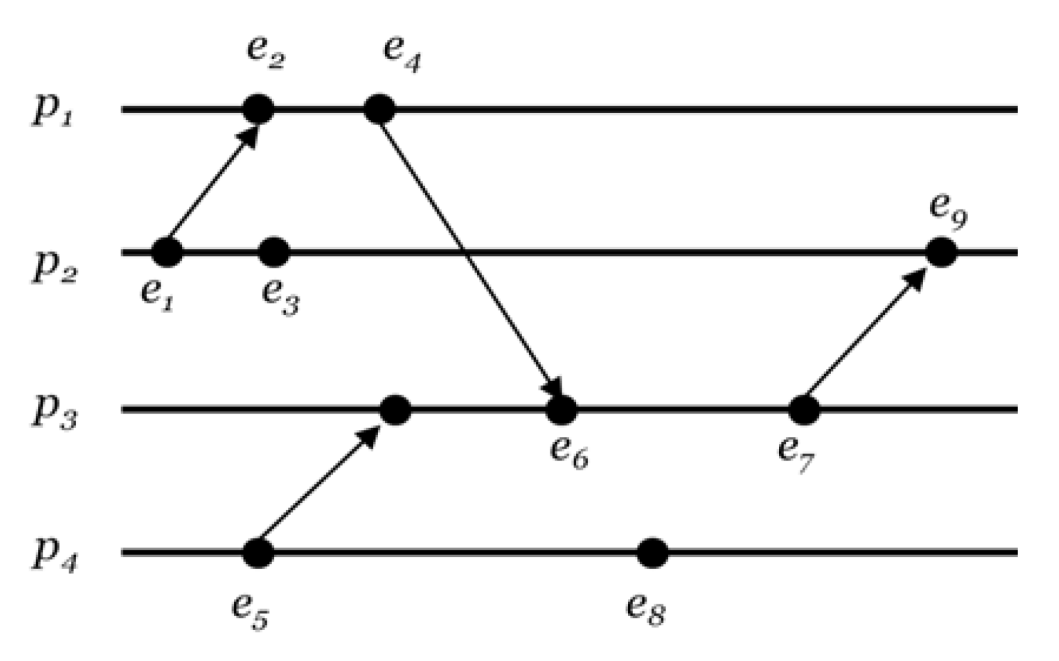
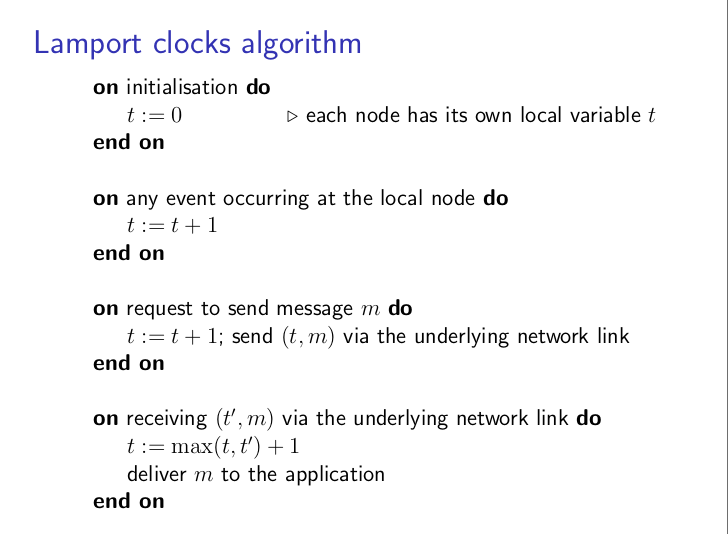
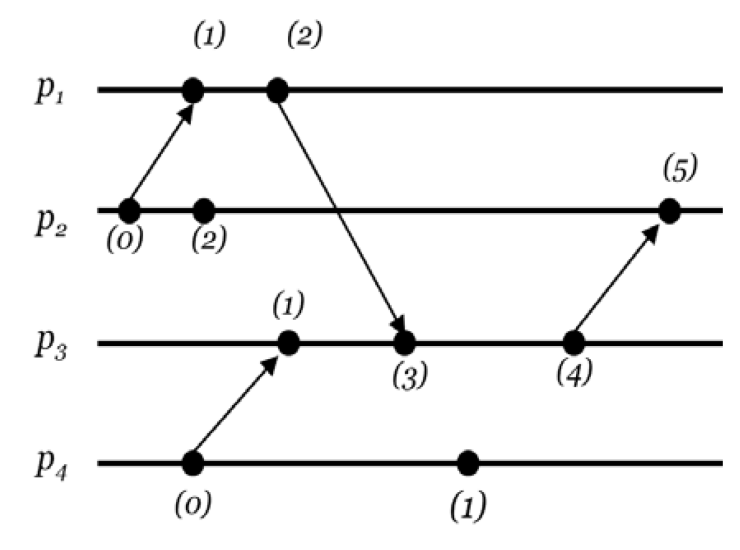
- e → f then clock(e) < clock(f)
If event e happend before event f, clock(e) < clock(f)
Improvement vector clocks
GCPGoat: Vulnerable by Design GCP Infrastructure
Source: https://github.com
GCPGoat is vulnerable to the GCP design infrastructure that allows attackers to test and improve their attacking skills by exploiting common misconfigurations and vulnerabilities, including XSS, server-side request forgery, weak storage bucket implementation, and IAM privilege escalation. Emulating real-world infrastructure, GCPGoat highlights the latest OWASP Top 10 web application security risks for 2021 and other typical misconfigurations in services such as IAM, storage buckets, cloud functions, and Compute Engine.
Attack Scenarios with GCPGoat
The following are various scenarios in which attackers can utilize GCPGoat to practice and hone their skills:
Server-Side Request Forgery (SSRF)
Perform an SSRF attack, fetch the source code file from the cloud function and dump the database to overtake the admin account of the target blog application.
Figure 19.131: Screenshot of Server-Side Request Forgery using GCPGoat
Misconfigured Storage Bucket Policies
Use the misconfigured bucket policies to gain admin access to one of the buckets.
Figure 19.132: Screenshot of exploiting misconfigured storage bucket policies using GCPGoat
Lateral Movement
Find the credential for a low privileged virtual machine instance from the dev bucket and then access other high privileged Compute Instances through that low privileged machine.
Figure 19.133: Screenshot of lateral movement via Compute Instances using GCPGoat