nmap - syn scan
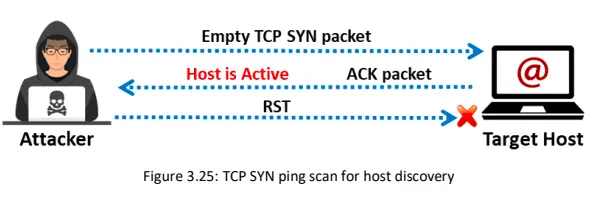
the TCP-SYN scan (-sS) is one of the default settings unless we have defined otherwise and is also one of the most popular scan methods. This scan method makes it possible to scan several thousand ports per second. The TCP-SYN scan sends one packet with the SYN flag and, therefore, never completes the three-way handshake, which results in not establishing a full TCP connection to the scanned port.
- If our target sends a
SYN-ACKflagged packet back to us, Nmap detects that the port isopen. - If the target responds with an
RSTflagged packet, it is an indicator that the port isclosed. - If Nmap does not receive a packet back, it will display it as
filtered. Depending on the firewall configuration, certain packets may be dropped or ignored by the firewall.