Kerberoasting
Kerberoasting is a post-exploitation attack technique that targets the Kerberos authentication protocol, commonly used in Microsoft Active Directory environments. It allows attackers to extract and crack service account credentials, facilitating privilege escalation and lateral movement within the network.
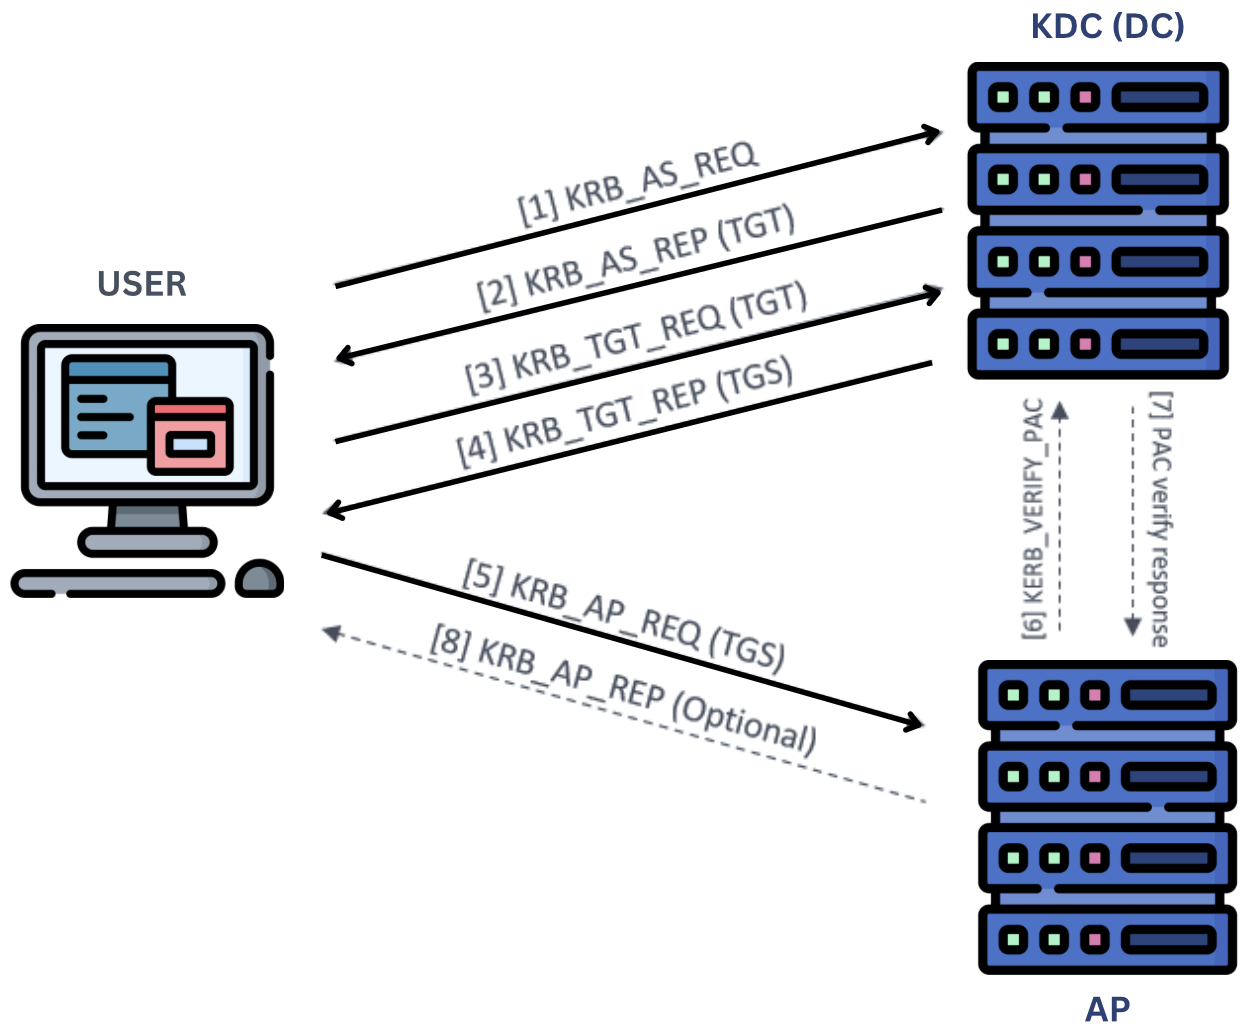
Methodology
- Service Principal Names (SPN) Enumeration
An attacker identifies Active Directory accounts with associated SPNs. These SPNs correspond to service accounts that authenticate services like SQL Server or IIS. - Requesting Service Tickets
Using tools like Rubeus or GetUserSPNs.py, the attacker requests Kerberos service tickets (TGS) for the identified SPNs. - Extracting and Cracking Tickets
The attacker extracts the service tickets and attempts to crack the encrypted password hashes offline using brute-force tools like Hashcat or John the Ripper. - Gaining Unauthorized Access
Once the plaintext password is obtained, the attacker can authenticate as the service account, gaining access to resources and systems associated with that account.