TCP - Termination
The query FIN refers to the Finish flag in the Transmission Control Protocol (TCP) header, which is crucial for reliably terminating a TCP connection. It is also utilized by attackers in various network scanning and evasion techniques.
Here is a detailed explanation of the FIN flag based on the sources:
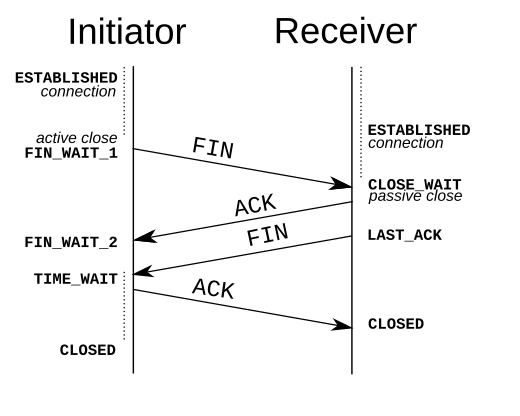
1. Definition and Role in TCP Communication
The FIN flag is one of the six control flags in the TCP header that manage the connection between two hosts.
- Function: When the
FINflag is set to "1", it announces that no more transmissions will be sent to the remote system and signals the termination of the connection that was established by theSYNflag. - Connection Termination: The
FINflag is part of the established procedure for ending a TCP session. After completing data transfers, the sender sends a connection termination request using aFINorRSTpacket. Upon receiving the request, the receiver acknowledges it with anACKpacket and then sends its ownFINpacket to complete the termination.
2. Exploitation in Network Scanning (Stealth Techniques)
Attackers leverage the FIN flag in stealth scanning methods because many security mechanisms, such as firewalls and Intrusion Detection Systems (IDS), are designed to detect the initial SYN packet used in traditional connection attempts.
A. FIN Scan
The FIN Scan is an Inverse TCP Flag Scan technique categorized as a Stealth TCP Scanning Method.
- Probe Packet: In a FIN scan, the attacker sends a probe packet with only the
FINTCP flag set. - Response Analysis (RFC 793 Compliance): This technique relies on the behavior defined by RFC 793 (the TCP standard) when handling packets without the
SYN,RST, orACKflags.- Open Port: If the port is open, the target host (if compliant with RFC 793, such as UNIX-based OSs) will drop the segment and send no response.
- Closed Port: If the port is closed, the target host will reply with an
RST(Reset) packet in response to the incoming segment.
- Tool Usage: In Zenmap, the
-sFoption is used to perform a FIN scan. - Disadvantage: This technique is not effective against Microsoft Windows hosts because Windows OSs ignore the RFC 793 standard concerning this behavior.
B. Xmas Scan
The FIN flag is also used as part of the Xmas Scan, another inverse TCP scanning technique.
- Probe Packet: The Xmas scan sets three flags in the probe packet:
FIN,URG(Urgent), andPSH(Push). This lights the packet up "like a Christmas tree". - Response: Similar to the FIN scan, if the port is open, there is no response; if the port is closed, the remote system replies with an
RSTpacket. - Tool Usage: In Zenmap, the
-sXoption is used to perform the Xmas scan.
3. Role in Denial-of-Service (DoS) Attacks
The FIN flag is also utilized by attackers in denial-of-service (DoS) and Spoofed Session Flood attacks:
- Spoofed Session Flood: Attackers create fake or spoofed TCP sessions by carrying multiple
SYN,ACK, andRSTorFINpackets. This attack bypasses firewalls that only monitor incoming traffic and exhausts the target's network resources.
